This guide breaks down multi-tenant SaaS architecture end-to-end: what it is, the three database models, real build costs, and how to implement tenant isolation without a data leak. Built for founders and CTOs deciding how to architect a SaaS product past its first 100 customers.
Key Takeaways
Multi-tenant architecture lowers cost by sharing one codebase and infrastructure across customers.
Three database models: pool, bridge, and silo balance cost and data isolation.
Global SaaS revenue is projected to reach $488.5B in 2026, growing 21.9% YoY.
Migrating from single-tenant to multi-tenant typically takes 3–6 months.
Your SaaS product just signed customer #50. Onboarding now means spinning up new infrastructure, and your DevOps bill is climbing faster than revenue.
This is the point where most SaaS teams realize their architecture decision from month one is now their biggest cost center.
This blog walks through what multi-tenant SaaS architecture actually is, the three database models to choose from, what each one costs to build and run, and how to migrate without breaking production.
Global SaaS revenue is projected to reach $488.5 billion in 2026, growing 21.9% year-over-year, according to Statista, and most of that growth runs on multi-tenant infrastructure.
What Is Multi-Tenant SaaS Architecture?
Multi-tenant SaaS architecture is a design where one application instance and one shared infrastructure layer serve multiple customer organizations, called tenants, while keeping each tenant’s data and configuration logically separated.
Every tenant runs on the same codebase instead of a separate deployment per customer.
This is different from single-tenant architecture, where each customer gets a dedicated, isolated deployment.
Salesforce, Slack, and Zendesk all run on variations of multi-tenancy; it’s why they can push one feature update to every customer at once, instead of coordinating hundreds of separate deployments.
What makes this more complex than it looks: isolation isn’t just a database column.
Tenant context has to be enforced consistently across authentication, caching, background jobs, file storage, and monitoring, not just wherever the data happens to sit.
Multi-tenancy is also not the same as multi-instance deployment, where a vendor runs separate copies of the same application per customer on shared cloud infrastructure.
Multi-instance still means separate deployments to patch and monitor; it saves on hardware, not on operational overhead, which is the real cost multi-tenancy removes.
Multi-Tenant vs Single-Tenant SaaS: What’s the Difference?
Multi-tenant SaaS shares one application and infrastructure layer across many customers with logical data separation. Single-tenant SaaS gives each customer a fully dedicated deployment.
The trade-off is straightforward: multi-tenant wins on cost and speed, single-tenant wins on isolation and customization.
Factor
Multi-Tenant
Single-Tenant
Cost per customer
Drops as tenant count grows
Stays roughly flat per customer
Onboarding speed
Minutes (a new tenant record)
Days to weeks (a new deployment)
Customization
Config-driven, limited
Full control per customer
Compliance fit
Works with strong RLS + audit logs
Easier to defend in strict reviews
Feature rollout
One deployment reaches everyone
Per-customer deployment coordination
Best fit
Horizontal SaaS, high tenant count
Regulated enterprise, low tenant count
Neither model is universally correct.
Most SaaS teams start pooled multi-tenant to keep costs down, then move specific enterprise or regulated accounts into a more isolated model once a real contract demands it.
What Are the Multi-Tenant Database Models? (Pool, Bridge, Silo)
Multi-tenant SaaS architecture uses three core database models: pool (shared schema), bridge (schema-per-tenant), and silo (database-per-tenant).
Each one sits at a different point on the spectrum between cost efficiency and data isolation.
AWS documents these same three patterns in its SaaS tenant-isolation guidance, and most production SaaS platforms map cleanly onto one of them, or a hybrid of two.
There is no single correct model. The right choice depends on your ARPU, your compliance obligations, and how much engineering time you have before your next funding milestone or enterprise deal.
Pool Model (Shared Schema)
In the pool model, every tenant shares the same database and the same tables.
A tenant_id column on every table filters which rows belong to which customer.
This is the cheapest model to run — one database, one set of indexes, one backup schedule.
It’s also the riskiest model from a security standpoint.
A single missing WHERE tenant_id =? clause in one query can expose one customer’s data to another.
Row-level security (RLS) policies in PostgreSQL close this gap by enforcing the filter at the database level, not just in application code.
Example: A project management SaaS platform with 5,000 small-business tenants runs the pool model with PostgreSQL RLS enabled on every table.
Because average revenue per tenant sits under $50 a month, running separate databases per tenant would erase the margin entirely; the pool model is the only one that keeps unit economics positive at that price point.
Bridge Model (Schema-per-Tenant)
In the bridge model, all tenants share one database server, but each tenant gets a dedicated schema.
This gives stronger isolation than the pool model without the full operational overhead of separate databases.
Backup and restore can happen at the schema level for a single tenant, which pool architectures can’t easily support.
The trade-off shows up as tenant count grows.
PostgreSQL typically caps useful connections in the low hundreds per instance, and schema-per-tenant setups burn through those connections faster than shared-schema setups.
Schema sprawl is the other real cost.
Once a migration has to run across 300-plus schemas, a change that used to take one deployment now takes 300 separate migration runs, each with its own chance to fail differently.
Example: A B2B HR platform ran the bridge model comfortably up to roughly 250 tenants, then hit connection-pool limits and moved its highest-usage tenants into dedicated databases.
Silo Model (Database-per-Tenant)
In the silo model, each tenant gets a dedicated database, sometimes on dedicated infrastructure.
Isolation here is physical, not logical.
One tenant’s slow query, oversized backup, or runaway migration can’t touch another tenant’s performance.
This is the model regulated industries reach for by default.
Healthcare and fintech compliance frameworks often require this level of separation as a baseline, not as an upgrade path.
The cost is real: every new tenant means a new database to provision, monitor, back up, and patch.
Cross-tenant analytics, answering “what’s our average usage across all customers”, becomes a distributed query problem instead of one SQL statement.
Example: A healthcare SaaS platform handling patient records for multiple clinics runs database-per-tenant by default, because HIPAA audit requirements make shared-schema isolation a harder case to defend during a compliance review.
Model
Isolation
Cost at Scale
Best For
Cons
Pool
Logical (tenant_id column)
Lowest
High tenant count, low ARPU
Bridge
Logical (dedicated schema)
Medium
Mid-market B2B, moderate compliance
Silo
Physical (dedicated database)
Highest
Regulated industries, enterprise accounts
How Does Tenant Isolation Actually Work?
Tenant isolation means enforcing a hard boundary between customers at every layer of the system: authentication, data access, background jobs, caching, and file storage — not only in the database.
A secure multi-tenant system authenticates the user, resolves their tenant ID, and applies that ID everywhere the request touches data.
Authentication: The session or token should carry the tenant ID as a first-class claim, checked on every request.
Data access: Row-level security or tenant-scoped ORM queries should enforce the boundary at the data layer, not just in business logic.
Caching: Redis keys must be tenant-namespaced. A cache key without a tenant prefix can silently serve one customer’s cached data to another.
Background Jobs: Async workers must carry tenant context through the entire job lifecycle, including retries and dead-letter queues.
File Storage: S3 paths or buckets should be scoped per tenant, with IAM policies enforcing the boundary, not just a naming convention.
Getting this right across every layer is where most in-house teams underestimate scope. It’s a big reason SaaS teams bring in a dedicated SaaS development partner rather than retrofitting isolation after launch, when a fix touches five different systems instead of one.
Real Benefits of Multi-Tenant SaaS Architecture
Multi-tenant architecture pays off in business outcomes, not just technical features.
Feature
Business Outcome
Shared infrastructure
The 1,000th customer costs a fraction of the 10th to serve, protecting margin as you scale.
One deployment
A feature ships to every customer the same day, instead of a multi-week rollout.
Config-driven onboarding
A new enterprise customer can go live in under an hour instead of a multi-day setup.
Unified usage data
Cross-customer analytics run as one query instead of an aggregation job.
These outcomes compound.
Faster onboarding means faster time-to-revenue on every new deal; unified analytics means product decisions get made on real usage data instead of anecdotes from a handful of accounts.
There’s also a hiring benefit that rarely gets mentioned: engineers can move between features without learning a new per-customer deployment quirk, since every tenant runs the same code path.
Real Multi-Tenant SaaS Examples (With Measurable Results)
Multi-tenant architecture isn’t theoretical; it’s what large-scale SaaS platforms actually run on, and the results are documented.
Firmex, a virtual data room provider, migrated 65,000 individual SQL Server databases into a consolidated multi-tenant architecture on Amazon Aurora PostgreSQL.
The migration took about 3 months with near-zero service disruption, and cut Firmex’s database operating costs by 75% (AWS case study).
SuperTokens re-architected its authentication infrastructure around dedicated tenant pools sharing one core instance.
The company reports the change cut its AWS infrastructure costs by roughly 50% (SuperTokens blog).
Zendesk applies the same isolation principle to its AI features, sharing inference infrastructure across tenants while keeping each customer’s model context isolated.
That architecture decision reduced Zendesk‘s ML inference costs by 90% without compromising per-tenant data separation (per eesel AI’s analysis of Zendesk’s architecture).
The pattern across all three: the savings come from sharing infrastructure, and the safety comes from enforcing isolation in software, not from splitting infrastructure per customer.
What Are the Risks and Challenges of Multi-Tenant SaaS?
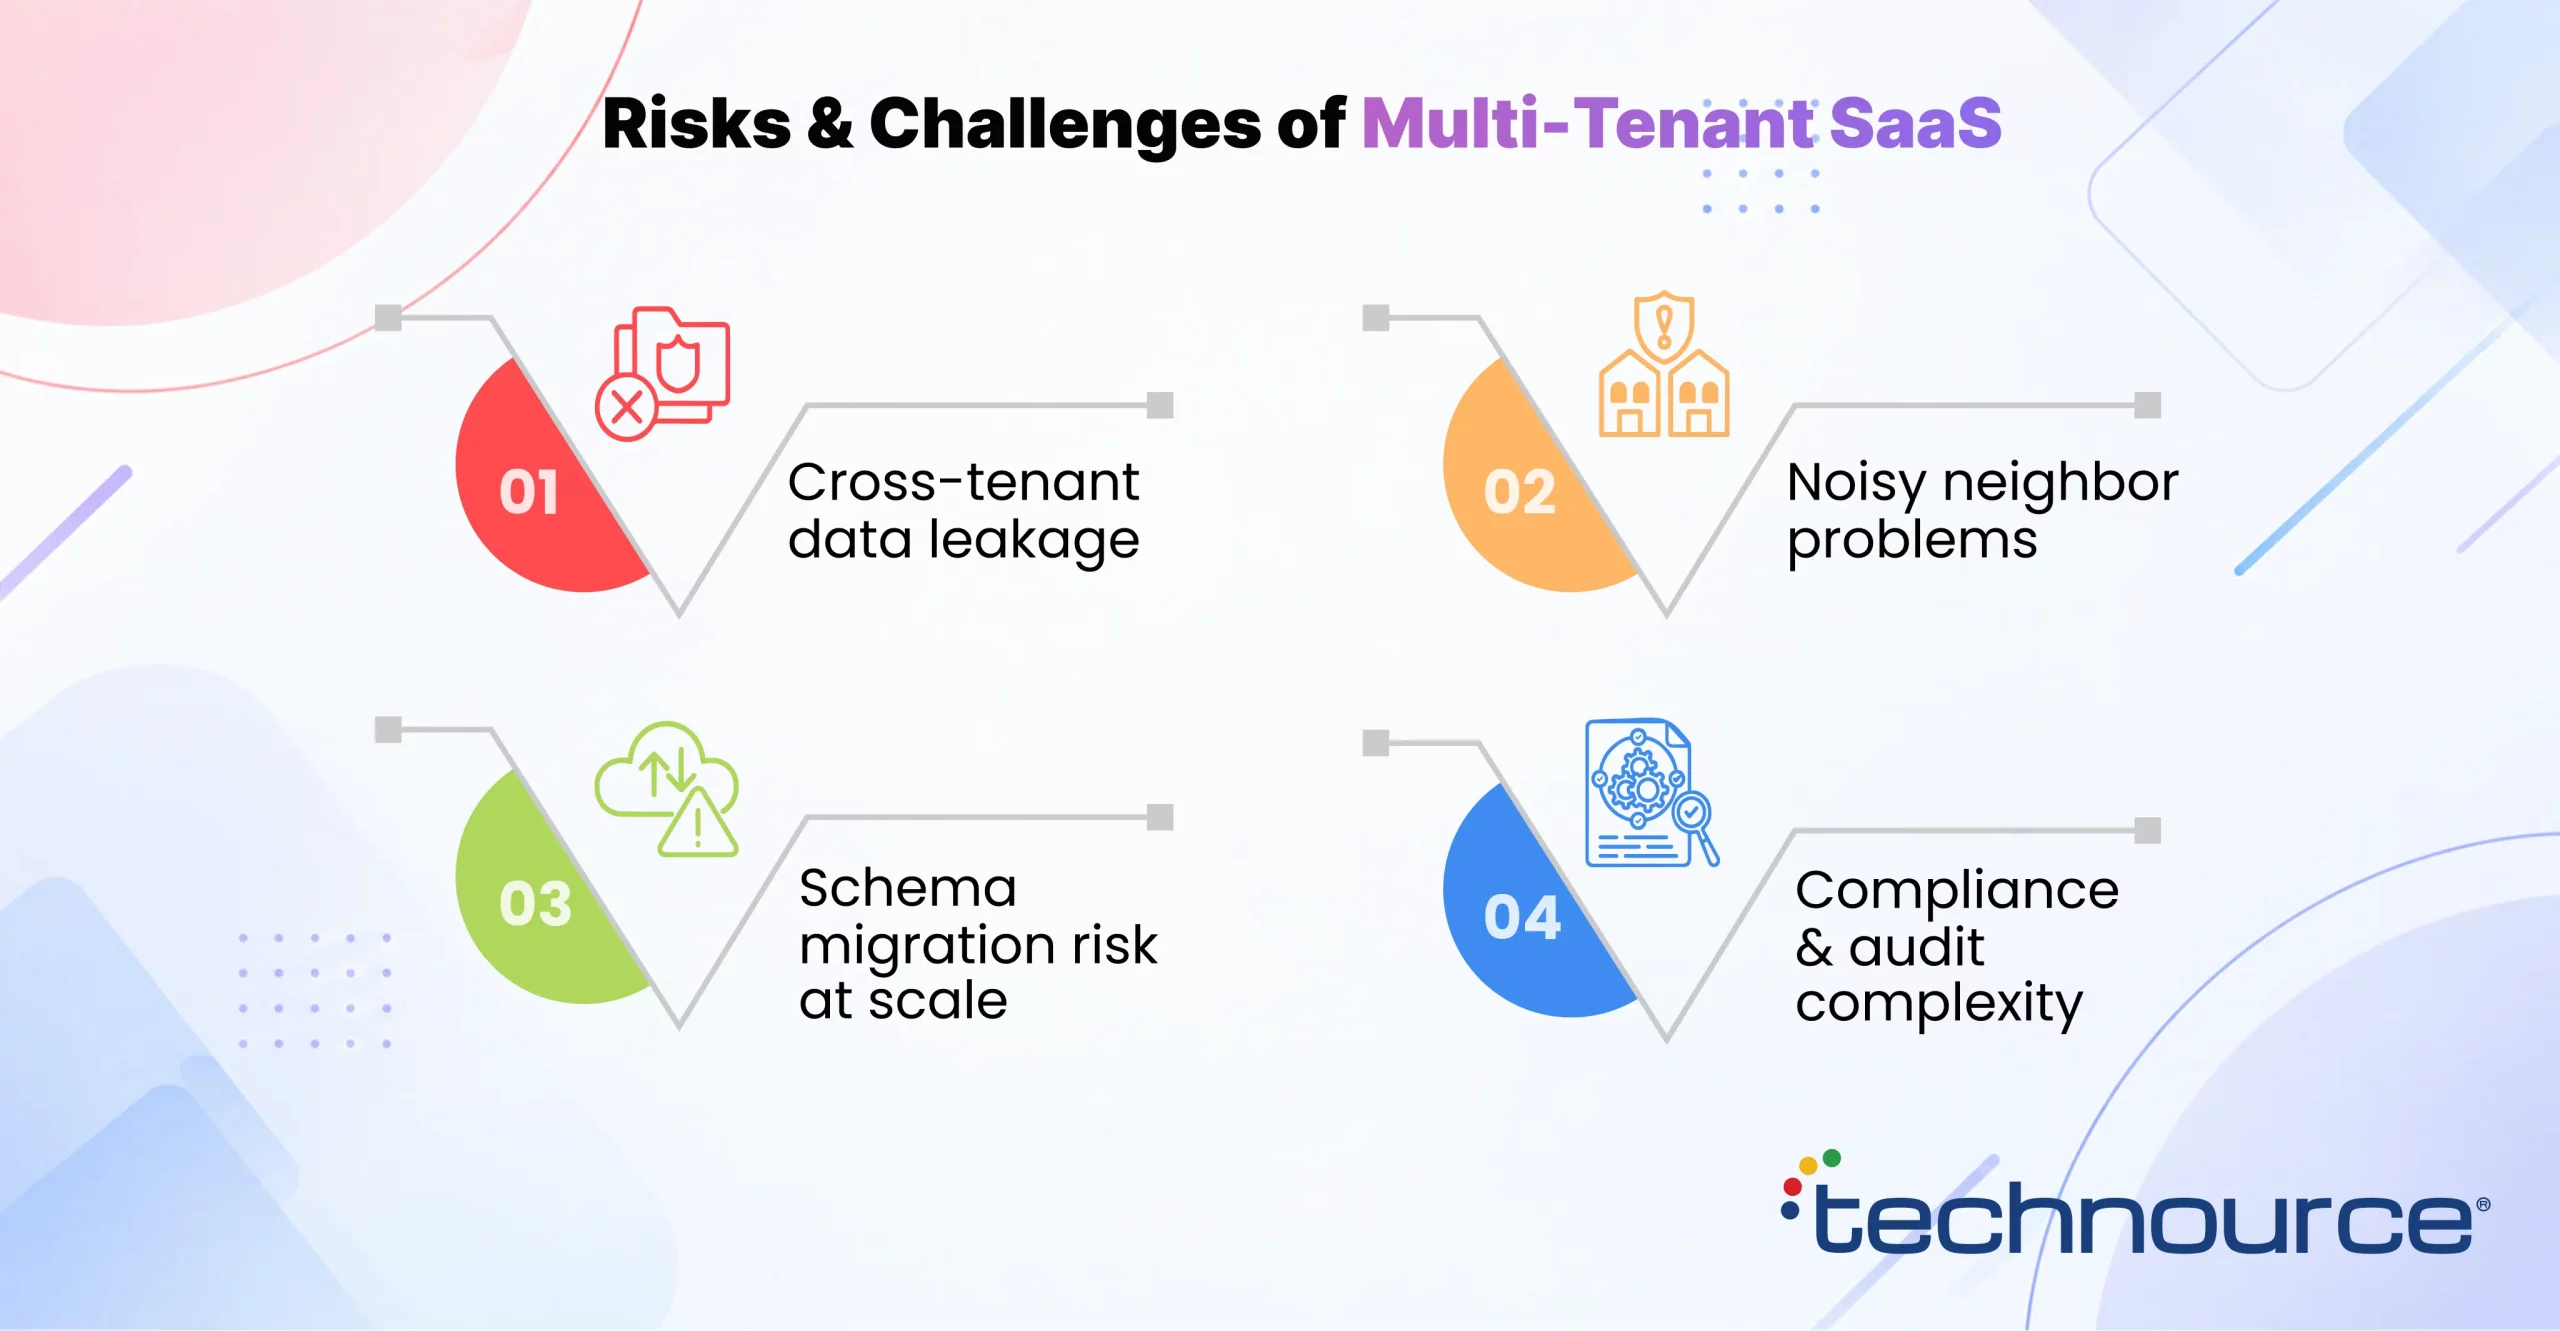
Multi-tenant architecture concentrates risk in the same place it concentrates savings: shared infrastructure. Three failure modes account for most production incidents.
Cross-tenant data leakage: A single missing tenant_id filter is the most common root cause of a data exposure incident in pooled architectures. Row-level security reduces this risk but doesn’t eliminate it if a new table ships without the policy applied.
Noisy neighbor problems: One tenant running a heavy report or batch job can slow queries for every other tenant sharing that database or schema. This gets worse, not better, as your largest customers grow.
Schema migration risk at scale: A migration that takes 10 minutes on one schema can take hours across 500 tenant schemas, and a failure partway through can leave tenants on inconsistent versions of your data model.
Compliance and audit complexity:Proving to an auditor that shared infrastructure actually keeps tenants separate takes more evidence than pointing at a dedicated server. Expect to document RLS policies, access logs, and encryption-at-rest configuration in detail during any SOC 2 or HIPAA review.
None of these risks are a reason to avoid multi-tenancy. They’re a reason to design isolation and monitoring from the start, not retrofit them after the first incident.
How to Implement Multi-Tenant SaaS Architecture: Step by Step
Step 1: Define your tenant isolation requirements first
Before writing any code, define what your top three customers will require 18 months from now, not just today.
A healthcare or fintech prospect will likely demand physical isolation regardless of your current tenant count.
Pull this from real sales and compliance conversations, not internal guesses.
What can go wrong: teams that skip this step build a pool model by default, then face a forced re-architecture the moment their first enterprise deal requires stronger isolation guarantees than the schema was built for.
Step 2: Pick one database model and commit to it for 12 months
Match the model to your actual customer profile: pool for high-volume, low-ARPU products; bridge for mid-market B2B; silo for regulated or enterprise accounts.
Switching models later costs 20–40% more in engineering time than building it right the first time, according to cloud migration studies.
What can go wrong: mixing models too early, before a specific contract demands it, adds complexity without paying off in revenue.
Step 3: Enforce tenant isolation at the database level, not just in application code
Use PostgreSQL row-level security policies so the database itself refuses cross-tenant rows, instead of trusting every developer to remember a WHERE clause.
Pair this with tenant-scoped ORM queries as a second layer of defense, not a replacement for RLS.
Our product engineering team treats this as a non-negotiable step in every multi-tenant build, not an optional hardening pass added later.
What can go wrong: relying on application-layer filtering alone means one missed filter in one endpoint exposes every tenant’s data; this is the single most common multi-tenant SaaS security failure in production.
Step 4: Extend tenant context through caching, jobs, and file storage
Namespace every Redis key, S3 path, and queue message with a tenant ID, and verify it in code review, not only at write time.
Background workers must carry tenant context through the entire job lifecycle, including retries and dead-letter queues.
What can go wrong: a cache key without a tenant prefix can silently serve one customer’s cached data to another, and this bug often surfaces only under production load, not in testing.
Step 5: Build tenant-aware monitoring before you need it
Tag traces, metrics, and logs with tenant ID from day one so you can isolate which customer is driving a performance issue.
Set per-tenant rate limits and quotas so one heavy user can’t degrade service for everyone else.
What can go wrong: without this, a single noisy tenant looks like a platform-wide outage, and your team spends hours debugging the wrong layer before finding the real cause.
How Much Does Multi-Tenant SaaS Architecture Cost to Build?
Build cost depends on the isolation model: a pooled-model MVP typically runs $40,000–$60,000, while a silo architecture with per-tenant infrastructure can exceed $150,000. Overall SaaS development cost also depends on the product’s features, integrations, security requirements, and technical scope.
Ongoing hosting costs stay flatter in pooled models as tenant count grows, while silo models scale hosting costs close to linearly per tenant.
Model
Typical Build Cost (MVP)
Hosting Cost Growth
Best Fit
Pool
$40,000–$60,000
Flattens fast as tenants scale
High-volume, low-ARPU SaaS
Bridge
$60,000–$90,000
Grows moderately with tenant count
Mid-market B2B SaaS
Silo
$90,000–$150,000+
Scales near-linearly per tenant
Regulated industries, enterprise
These are engineering estimates for the isolation layer itself, auth, RLS policies, tenant-aware caching, and monitoring, not the full product build.
Ongoing costs add up beyond hosting: expect budget for per-tenant monitoring tooling, periodic security audits, and the engineering time to review every new feature for cross-tenant exposure before it ships.
What Tech Stack and Scaling Path Should You Use?
A typical multi-tenant SaaS stack pairs PostgreSQL with row-level security, Redis for tenant-namespaced caching, and a job queue that carries tenant context through every async task.
The stack doesn’t need to change as you scale, but how you configure it does.
Monitoring tools like Datadog or Grafana should be configured with tenant ID as a dimension from day one, so a per-customer dashboard is a filter, not a rebuild.
Without that dimension baked in early, retrofitting per-tenant visibility later usually means re-instrumenting every service that touches tenant data.
Shared by tenant, move top accounts to hybrid silo
Planning this scaling path early avoids a costly re-architecture later.
Our cloud and DevOps team builds this tenant-aware scaling into the infrastructure from day one, instead of bolting it on after the first outage.
Should You Build or Buy Multi-Tenant Infrastructure?
Buying tenant-management infrastructure from a vendor like Frontegg, WorkOS, or SuperTokens saves 2–3 months of engineering time but adds a recurring per-tenant or per-user fee.
Building it in-house costs more upfront but removes that recurring cost and gives full control over the isolation model.
Option
Best For
Key Limitation
Estimated Cost
Buy (Frontegg, WorkOS, SuperTokens)
Fast launch, small engineering team
Recurring fees, less control
$500–$3,000/month at scale
Build in-house
Long-term products, specific compliance needs
Slower launch, ongoing maintenance
$40,000–$90,000 upfront
Most early-stage teams buy first and revisit the decision once tenant count or compliance requirements outgrow the vendor’s model.
A simple heuristic: if you’re pre-product-market-fit, buy and move fast. If tenant isolation is core to your competitive moat or compliance story, build it in-house from the start.
What’s Next for Multi-Tenant SaaS Architecture?
Regional multi-tenancy is becoming standard as data residency laws tighten.
Mature SaaS products increasingly route tenants to region-specific infrastructure instead of one global shared pool, treating region as a first-class field on the tenant record rather than an infrastructure afterthought.
AI features are pushing tenant isolation into the inference layer, not just the database.
Zendesk’s approach, sharing infrastructure while isolating model context per tenant, is becoming the reference pattern for SaaS platforms adding AI features on top of existing multi-tenant systems.
Global SaaS revenue is projected to keep growing at roughly 21.9% year-over-year through 2026, according to Statista, which keeps pushing more vendors toward multi-tenant models to protect margin at scale.
Hybrid tenancy is also gaining ground as a default, not an edge case. Mixed models — pooled infrastructure for most customers, dedicated resources for high-value or regulated accounts — let SaaS providers serve both ends of the market from one platform.
Expect more platforms to offer tenant isolation as a paid tier, rather than an all-or-nothing architectural choice baked in at launch.
Why Choose Technource for Multi-Tenant SaaS Development?
Multi-tenant architecture requires more than sharing infrastructure; it requires tenant isolation to be designed into every layer of the product.
With 13+ years of experience and 1,000+ projects delivered, Technource builds SaaS platforms with tenant isolation, scalability, and long-term operating costs in mind.
Tenant-aware infrastructure: Tenant context carried across authentication, caching, background jobs, file storage, and monitoring.
Architecture matched to your business: Pool, bridge, silo, or hybrid models based on tenant count, ARPU, compliance, and growth plans.
AI-ready foundations: Tenant isolation extends to AI-powered workflows and features as they are introduced.
Scale-ready engineering: Architecture decisions are made with future tenant growth and operational complexity in mind.
Rather than defaulting to the most expensive architecture, we help you choose an isolation model that meets your security and compliance requirements while remaining practical to operate as your customer base grows.
Conclusion
Multi-tenant SaaS architecture is a spectrum, not a single decision.
Pool, bridge, and silo models each fit a different stage, customer profile, and compliance requirement.
The three takeaways that matter most: isolation has to be enforced at every layer, not just the database; the model you pick early is expensive to change later; and most teams underestimate the operational cost until they hit their first 500 tenants.
Next step: map your tenant isolation requirements against your next 12 months of sales conversations before you write a line of schema. If you need help translating those requirements into a scalable architecture, SaaS development services can provide the engineering expertise to build the right foundation from the start.
FAQs
One application instance and shared infrastructure serve multiple customer organizations, each with logically isolated data. It’s the standard model behind most modern B2B SaaS platforms, including Salesforce and Slack.
Multi-tenant shares one codebase and infrastructure across customers with logical separation. Single-tenant gives each customer a fully dedicated deployment, trading cost efficiency for isolation.
Pool (shared schema with tenant_id columns), bridge (schema-per-tenant), and silo (database-per-tenant). Each trades infrastructure cost against isolation strength.
Yes, when tenant context is enforced at every layer — auth, data, caching, and jobs — not just the database. Row-level security policies remove reliance on application code alone.
Costs typically range from $40,000–$60,000 for a pooled-model MVP to $150,000+ for silo architectures with per-tenant infrastructure. Hosting costs stay flatter in pooled models as tenant count grows.
Yes, but expect 3–6 months of dedicated engineering work for a mid-sized product. Firmex migrated 65,000 single-tenant databases to a multi-tenant model in about 3 months (AWS case study).
Tenant isolation is the enforced boundary that keeps one customer’s data, config, and traffic separate from another’s. Without it, a single missing filter can expose one customer’s data to another.
No. Multi-instance runs a separate application copy per customer on shared cloud hardware, so patching and monitoring still happen per customer. True multi-tenancy shares one running application instance across all customers.